|
CIS Microsoft Windows 10 Enterprise Benchmark v5.0.0 |
🗏 18 Administrative Templates (Computer) | 18.6 Network | 18.6.8 Lanman Workstation
18.6.8.1 Ensure 'Enable insecure guest logons' is set to 'Disabled' (Level 1)
Created:2022/11/17 | Revised:2022/11/17
Overview
18.6.8.1 'Enable insecure guest logons' policy setting recommended state is 'Disabled'
Description
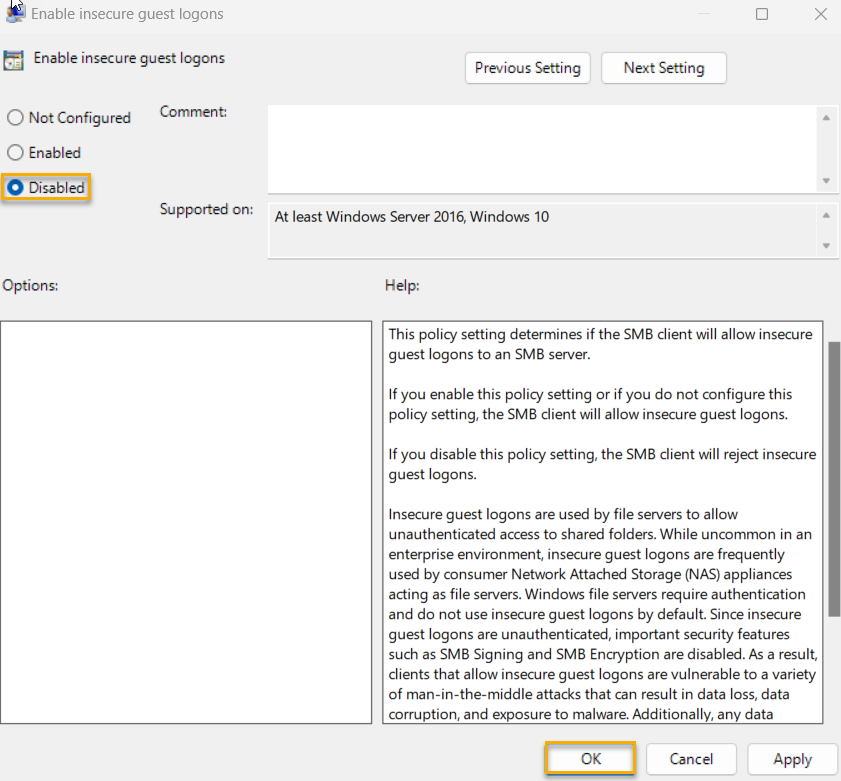
This policy setting determines if the SMB client will allow insecure guest logons to an SMB server.
The Server Message Block (SMB) protocol provides the basis for file and print sharing and many other networking operations.
Impact
Insecure guest logons are used by file servers to allow unauthenticated access to shared folders. While uncommon in an enterprise environment, insecure guest logons are frequently used by consumer Network Attached Storage (NAS) appliances acting as file servers.
Clients that allow insecure guest logons are vulnerable to a variety of man-in-the-middle attacks that can result in data loss, data corruption, and exposure to malware. Additionally, any data written to a file server using an insecure guest logon is potentially accessible to anyone on the network.
Solution
|
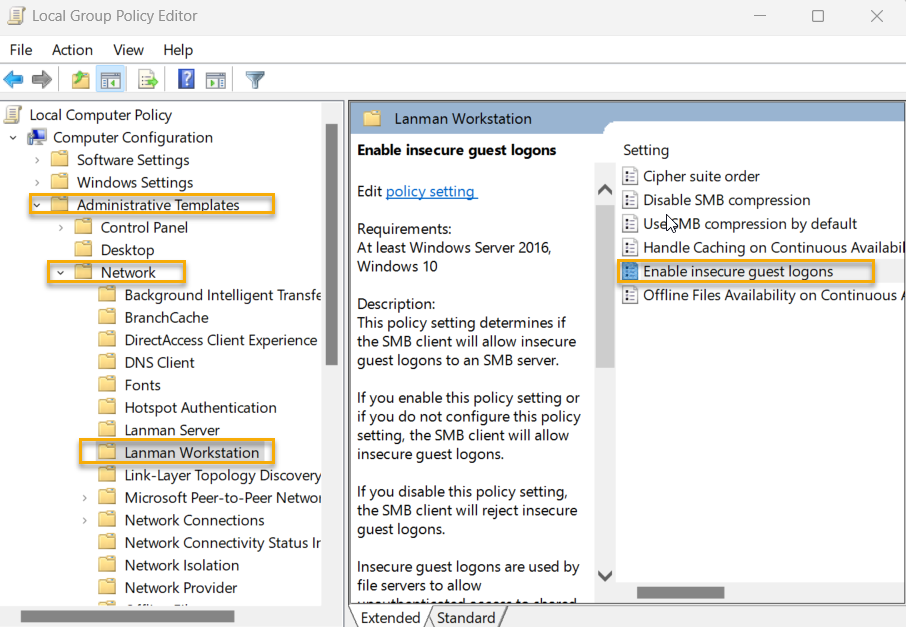
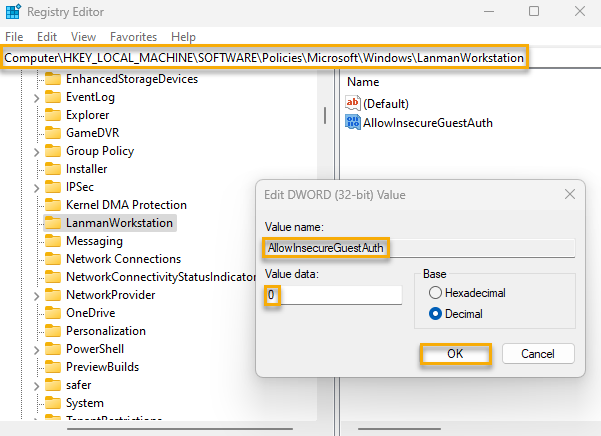
To configure the policy as recommended follow the steps below (choose one of the suggested ways): Fix using the consoleThis vulnerability can be automatically fixed within the console. Check the example of Automated Remediation Workflow implementation. Using Local Group Policy Editor
This Group Policy path may not exist by default. It is provided by the Group Policy template LanmanWorkstation.admx/adml that is included with the Microsoft Windows 10 Release 1511 Administrative Templates (or newer). Follow the link for download: Administrative Templates (.admx) for Windows 10 November 2021 Update [21H2] Using the Registry Editor
HKLM:\Software\Policies\Microsoft\Windows\LanmanWorkstation
AllowInsecureGuestAuth Set its value to 0
|